American Cities Hit by Ransomware

AUSTIN – The Department of Information Resources (DIR) is leading the response to a coordinated ransomware attack that has impacted at least twenty local government entities across Texas

​AUSTIN – The Department of Information Resources (DIR) is leading the response to a coordinated ransomware attack that has impacted at least twenty local government entities across Texas.

The Texas Division of Emergency Management is assisting by coordinating state agency support through the Texas State Operations Center.
Currently, DIR, the Texas Military Department, and the Texas A&M University System’s Cyberresponse and Security Operations Center teams are deploying resources to the most critically impacted jurisdictions.  Further resources will be deployed as they are requested.
Local jurisdictions who have been impacted should contact their local TDEM Disaster District Coordinator. DIR is fully committed to respond swiftly to this event and provide the necessary resources to bring these entities back online.
***

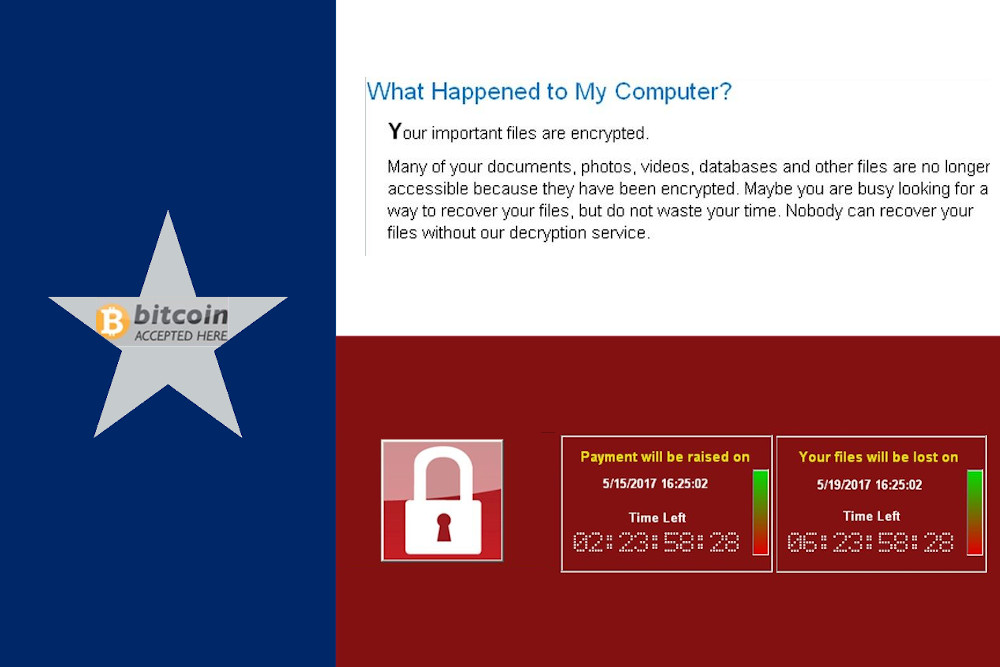
Users are then extorted for cash in order to regain access to their systems, and they are nearly always asked to pay in Bitcoin, a blockchain currency that is virtually untraceable, allowing hackers to pull off these complex operations from a single room halfway around the world.

It is unknown how much the hackers were demanding from Texas officials, which systems are currently offline and whether the impacted cities are expected to pay the ransom.

*** More than 20 Texas cities and towns have been taken ... photo

The attack took place on Friday morning, August 16, US time, when several smaller local Texas governments reported problems with accessing their data to the Texas Department of Information Resources (DIR).

DIR officials did not publish a list of impacted local governments. On Friday, the agency couldn’t provide an exact number of impacted entities, but a day later, DIR said the number is 23.

“It appears all entities that were actually or potentially impacted have been identified and notified,” DIR said. “Responders are actively working with these entities to bring their systems back online.”

The organization has been coordinating recovery efforts together with more than ten other Texas and US government agencies, such as the Texas Division of Emergency Management, the FBI, the DHS, the Texas Department of Public Safety, and others.

“At this time, the evidence gathered indicates the attacks came from one single threat actor,” DIR officials said on Saturday.

.JSE ransomware

ZDNet has learned from a local source that the ransomware that infected the networks of the 23 local Texas governments encrypts files and then adds the .JSE extension at the end.

This ransomware strain does not have its own name, being generally called the .jse ransomware –although some antivirus vendors detect it as Nemucod, under the name of the trojan that drops it on infected hosts.

First signs of this .jse ransomware have been spotted as early as August 2018, but activity has continued and has been reported as recently as this month. The ransomware is a strange one as it does not leave a ransom note behind, confusing victims who most of the time don’t know what happened.

In recent months, US cities have been a prime target for ransomware gangs, with infections reported all over the US.

In July, the governor of Louisiana declared a state emergency after a similar coordinated ransomware attack hit several school districts.
4 Russian Nuclear Monitor Stations, Gone Dark

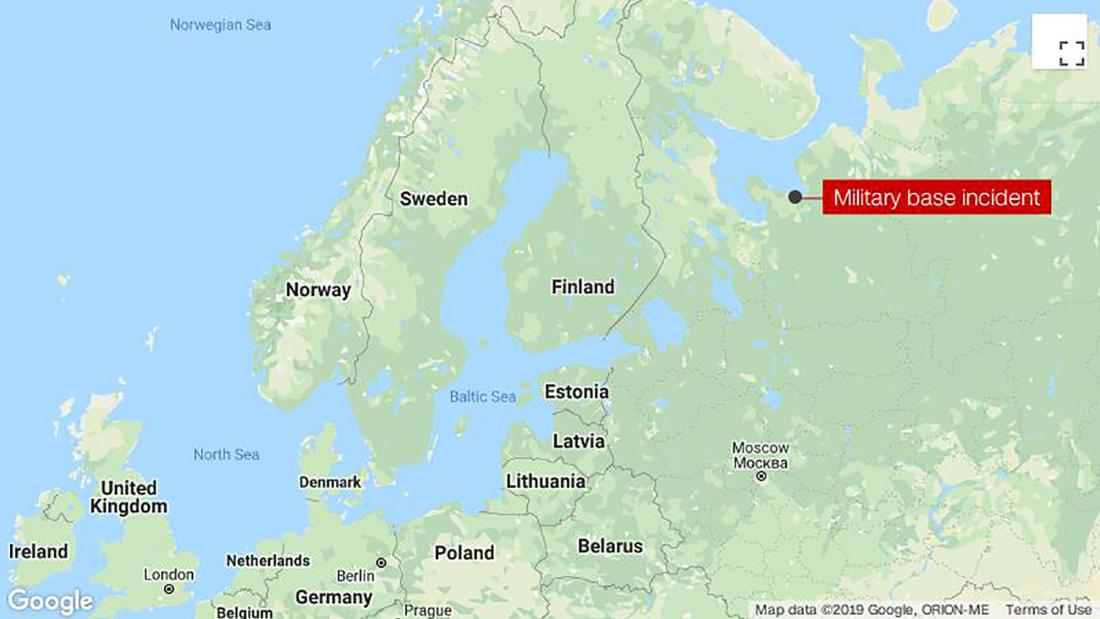
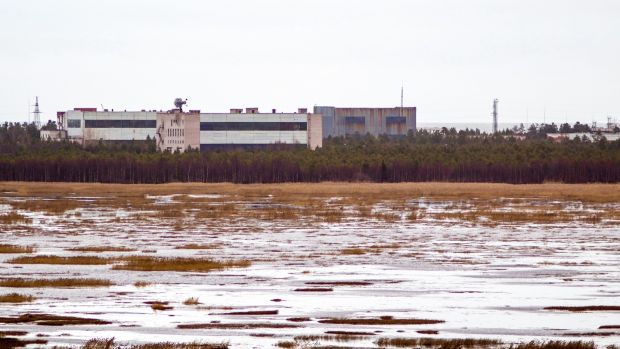
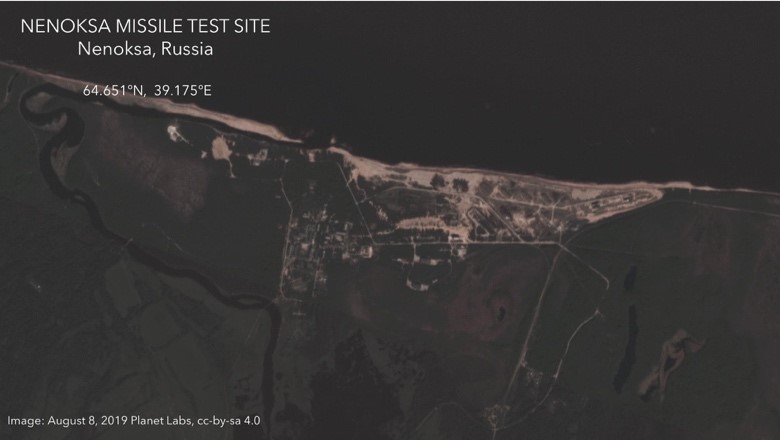
Severodvinsk is a well known Naval Testing Range and Russia is concealing data after the explosions at the missile test site.

Two Russian nuclear monitoring stations—specifically designed to detect radiation— “went silent” in the days following an explosion of what many believe was a nuclear-powered missile earlier this month during tests at a remote base, a nuclear official said in an email Sunday.

Lassina Zerbo, the head of the Comprehensive Nuclear Test  Ban Treaty Organization, told The Wall Street Journal in an email that two days after the explosion that the monitoring stations in Kirov and Dubna suffered “communication and network issues.”
Explosions rock Russian ammunition depot in Siberia – YouTubehttps://www.youtube.com

There have been reports that Russia has not been fully transparent about what occurred at a military base in the far northern Arkhangelsk region. The initial report from the country’s nuclear agency said that five workers were killed in a rocket engine explosion. The Guardian reported that radiation levels in Severodvinsk, a nearby city, increased 20 times above normal for about a half hour after the explosion. More here.

Related image photo

FPRI has more detail in part:

Why would Russia stake its prestige on a weapon system that the United States abandoned in the early 1960s? One reason might be a nuclear-powered cruise missile’s asymmetric deterrence impact, which given unlimited range, could alleviate “some of the difficulties associated with this medium/long range challenge, helping the Russians navigate around pockets of NATO aerospace and sea control to strike at assets supporting NATO and U.S. force projection,”[18] writes Ryan Kuhns, a Program Analyst with the National Nuclear Security Administration’s Defense Programs.

The Severodvinsk incident might have been a Burevestnik prototype test gone wrong. While from an engineering perspective, it is certainly possible with a nuclear thermal reactor based on a solid uranium core, a liquid radioisotope core, or even gaseous uranium to use thermal energy generated from radioactive decay to heat liquid hydrogen fuel, such technologies are unproven with regard to missiles.

On the other hand, the limited facts that exist in the public domain support an alternate, more plausible thesis: if a radioisotopic power system was involved and a liquid-fuel engine exploded, the Severodvinsk incident might well have been a Russia space program test gone wrong, possibly involving a small, uranium-235 based fission reactor. The Severodvinsk venue makes sense: the Russian Navy was involved in the country’s space program in the 1990s and 2000s. There is ample technical precedent as well. In April 1965, the United States successfully flight tested a flight-qualified fission reactor, the SNAP (Space Nuclear Auxiliary Power) 10A. The SNAP 10A converted heat from radioactive decay directly into electricity by means of a radioisotope thermoelectric generator (RTG). The radioactive isotope strontium-90, for example, has been used in both American and Russian RTGs.

If true, it could be suggested the Russian government used a false Burevestnik accident narrative to support a larger, perhaps equally fictitious one regarding Russian missile prowess and the penetrability of Western anti-missile defense. The Office of the Secretary of Defense’s 2019 Missile Defense Review[19] noted that “Russian strategy and doctrine emphasize the coercive and potential military uses of nuclear weapons, particularly including nuclear-armed, offensive missiles”:

Russian leaders also claim that Russia possesses a new class of missile, the hypersonic glide vehicles (HGV), which maneuver and typically travel at velocities greater than Mach 5 in or just above the atmosphere. . . . Russian leaders also claim that Russia possesses a new class of missile, the hypersonic glide vehicle (HGV), that enables Russian strategic missiles to penetrate missile defense systems. HGVs challenge missile defense capabilities because they are maneuvering vehicles that typically travel at velocities greater than Mach 5 and spend most of their flight at much lower altitudes than a ballistic missile. [20]

Russia’s hypersonic Nuclear Explosions


It appears there have been at least two explosions.

Several are dead, several are injured and total evacuations of nearby towns are underway due to extreme radiation levels being tested by bordering countries. Our own military and intelligence agencies are participating in countless meetings to review data, intelligence and evidence.

At issue is the work Russia is performing by placing a new nuclear reactor on hypersonic missiles and testing a jet propulsion system.

Remember, Vladimir Putin told the world about this several months ago.

The center of these operations is in Sarov, Russia, hosting a facility that somewhat emulates our own Los Alamos. This is not a new secret city as during the height of the Cold War, it was known to the United States as Arzamas-16. At this location, a nuclear powered cruise missile is being developed and tested called the Burevestnik. NATO refers to it as the SCC-X-Skyfall.

Authorities in northern Russia detected a brief rise in radiation levels following an explosion at a military training ground there, Russian state news agency TASS reported Thursday.
Severodvinsk has a naval base and shipyard and TASS, citing emergency services, initially said the incident began onboard a ship.
Image result for Severodvinsk

Russian authorities admitted that radiation levels in the city of Severodvinsk were up to 16x the normal rate after a nuclear reactor exploded last week. Five nuclear scientists died in the blast. Iodine was quickly distributed to panicked residents but supplies are now empty.

Russia has several nuclear cities (per NTI) so look for activity in other locations due to these explosions, at least our own intelligence agencies will be doing that.

Sarov (location of VNIIEF-Federal Nuclear Center and Avangard Electromechanical Plant). Formerly known as Arzamas-16.
Snezhinsk (location of VNIITF-Federal Nuclear Center). Formerly known as Chelyabinsk-70.
Zarechnyy (location of Start Production Association). Formerly known as Penza-19.
Novouralsk (location of Ural Electrochemical Combine). Formerly known as Sverdlovsk-44.
Lesnoy (location of Elektrokhimpribor Combine). Formerly know as Sverdlovsk-45.
Ozersk (location of Mayak Production Association). Formerly known as Chelyabinsk-65.
Trekhgornyy (location of Instrument Making Plant). Formerly know as Zlatoust-36.
Seversk (location of Siberian Chemical Combine). Formerly know as Tomsk-7.
Zheleznogorsk (location of Mining and Chemical Combine). Formerly known as Krasnoyarsk-26.
Zelenogorsk (location of Electrochemical Plant). Formerly known as Krasnoyarsk-45.

Fancy Bear, APT28, IoT, Hacking via Printers

Image result for jon huntsman moscow photo

Primer: U.S Ambassador to Russia, Jon Huntsman just issued his letter of resignation to President Trump. He states that he wants to return home to Utah due to a growing family. Gotta wonder if Amb. Huntsman ever really challenged Moscow on hacking and security intrusions of the United States.

Image result for fancy bear russia

MIT: A group of hackers linked to Russian spy agencies are using “internet of things” devices like internet-connected phones and printers to break into corporate networks, Microsoft announced on Monday.

Fancy Bear never hibernates: The Russian hackers, who go by names like Strontium, Fancy Bear, and APT28, are linked to the military intelligence agency GRU.

The group has been active since at least 2007. They are credited with a long list of infamous work including breaking into the Democratic National Committee in 2016, the crippling NotPetya attacks against Ukraine in 2017, and targeting political groups in Europe and North America throughout 2018.

Insecurity of Things: The new campaign from GRU compromised popular internet of things devices including a VOIP (voice over internet protocol) phone, a connected office printer, and a video decoder in order to gain access to corporate networks. Microsoft has some of the best visibility into corporate networks on earth because so many organizations are using Windows machines. Microsoft’s Threat Intelligence Center spotted Fancy Bear’s new work starting in April 2019.

The password is password: Although things like smartphones and desktop computers are often top of mind when it comes to security, it’s often the printer, camera, or decoder that leaves a door open for a hacker to exploit.

In multiple cases, Microsoft saw Fancy Bear get access to targeted networks because the IoT devices were deployed with default passwords. In another case, the latest security update was not applied. Using those devices as a starting point, the hackers established a beachhead and looked for further access.

“Once the actor had successfully established access to the network, a simple network scan to look for other insecure devices allowed them to discover and move across the network in search of higher-privileged accounts that would grant access to higher-value data,” Microsoft warned in a blog post published on Monday.

The hackers moved from one device to another, establishing persistence and mapping the network as they went, communicating with command and control servers all the while.

Global targets: Microsoft has been closely watching this group over the last year.

Of the 1,400 notifications the company delivered to those targeted or compromised by Fancy Bear, 20% have been to global non-governmental organizations, think tanks, or politically affiliated organizations. The remaining 80% have been to various sectors including government, technology, military, medicine, education, and engineering.

“We have also observed and notified STRONTIUM attacks against Olympic organizing committees, anti-doping agencies, and the hospitality industry,” Microsoft’s blog warned.

Last year, the FBI took disruptive action against a Fancy Bear campaign known as “VPNFilter” which targeted routers and network storage devices with malware with destructive capabilities of “bricking” a device by deleting firmware and rendering the device unusable. That campaign especially targeted Ukraine, a favorite target of Fancy Bear.

When Russia Helps N Korea Cheat on Sanctions, What to Do

Primer: Do you wonder what Russia’s votes on the UNSC really do to help North Korea? Do you wonder about the 40,000+ North Korean slave laborers in Russia add to the North Korean economy each year? About $200 million. How about the Russian oil pipeline that goes through North Korea? What about the rail system between the two countries and how that helps North Korea skirt sanctions with illicit goods transportation? Then there is the alleged legitimate navy and fishing fleets between Russia and North Korea. Money? Or the weekly air flight service from Vladivostok to Pyongyang. Or how Russia provides internet service to North Korea in addition to China, known as SatGate and the fiber optic lines that run along the rail system. Check front companies in China, Singapore and the banking system known as Dalcombank or just flying cash twice a week.

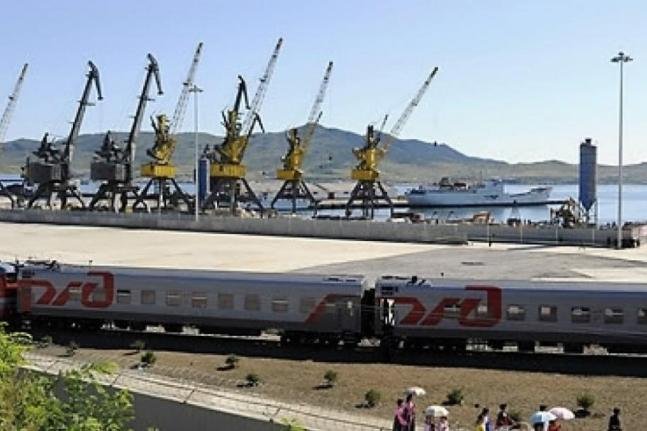
Rajin, North Korea Image result for rajin north korea  Image result for rajin north korea

FDD: The Treasury Department on Monday sanctioned a North Korean trading company official for helping Pyongyang evade U.S. and UN sanctions through illicit activity in Vietnam. The designation, which arrived in the brief interval between two North Korean missile tests in less than a week, suggests that Washington understands the importance of investigating and disrupting North Korea’s extensive overseas illicit networks.

Treasury’s latest target is Kim Su Il, who works for a Vietnam-based trading company on behalf of North Korea’s Munitions Industry Department, which the U.S. and UN have both sanctioned. According to Treasury, Kim helped export UN-sanctioned goods such as anthracite coal, titanium ore concentrate, and other raw materials from North Korea to Vietnam. Both anthracite coal and titanium ore are among the top exports that fund the regime’s illicit activities. Treasury also found that Kim Su Il helped charter ships and export Vietnamese products to North Korea, as well as to China and other undisclosed countries.

Kim Su Il’s designation is a reminder that North Korea’s overseas networks continue to thrive despite sanctions. In January, The Wall Street Journalreported that up to six Chinese-owned vessels transported North Korean coal between North Korea and Vietnam throughout 2018. In March 2018, the UN Panel of Experts also found that North Korean coal shipments to Vietnam go as far back as January 2017 – eight months before the UN Security Council’s comprehensive coal ban on North Korea went into effect. This persistent trade affirms Assistant Secretary of the Treasury Marshall Billingslea’s assessment in 2017 that coal “has been the center of North Korea’s revenue generation” for many years.

In March 2019, the same UN Panel of Experts exposed North Korea’s numerous overseas illicit money-making schemes, which employ networks of front companies, North Korean government workers, and local banks. For example, in Malaysia, North Korea’s intelligence agency, the Reconnaissance General Bureau, operated two companies that provided revenue to Pyongyang: the Malaysia-Korea Partners Group and Global Communications.

The UN Panel also found that foreign governments were applying “insufficient scrutiny” on the activities of North Korea’s overseas banking and government representatives, thereby enabling these company networks to thrive. The lax monitoring has ultimately allowed Pyongyang’s representatives to conduct financial transactions across numerous borders. Chinese banks in particular have been key enablers of North Korea’s actions.

Treasury provided robust evidence of this lax oversight last month when it sanctioned the Russian Financial Society (RFS) for helping North Korea evade sanctions. This designation revealed how a U.S.-sanctioned North Korean banking representative in Moscow exploited local financial service providers, specifically RFS, to conduct business for sanctioned North Korean companies. The incident showed that designating only the North Korean nationals working abroad is not enough. Rather, Washington also should target the banks and financial institutions that allow North Korean government officials based overseas to thrive.

Treasury’s next steps therefore should focus on investigating Kim Su Il’s local network of companies, individuals, and banks. Closing these gaps in enforcement is an indispensable step for maximizing the impact of U.S. sanctions on North Korea.